Privacy & Data Security

TEFCA’s October 26 compliance deadline is directed at QHINs, but organizations connected through them should be paying attention, too. A restriction further up the network could disrupt your access even if your organization followed the rules. With federal oversight expanding and data access disputes landing in court, participants may also need to explain what happened to records they exchanged long before this deadline.
Continue Reading TEFCA Sets October 26 Compliance Deadline for IAS as Federal Oversight Expands
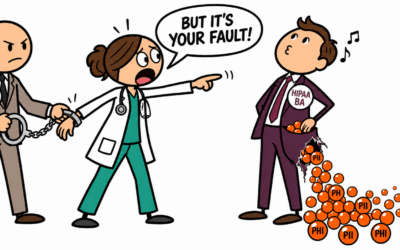
The breach happened at Labcorp’s debt collector, but Labcorp still agreed to pay nearly $2.3 million to the States. So, before you hand over those PHI marbles, ask yourself: if your vendor spills them, does your contract require it to help pay for the cleanup?
Continue Reading “But It Was Our Vendor’s Breach!” Labcorp’s $2.3 Million Settlement Puts Business Associate Oversight Back Under the Microscope

TEFCA’s Individual Access Services (IAS) rules are getting an update! Effective August 3, 2026, the revised requirements aim to help patients obtain their health records while strengthening identity verification and secure access. What changes for apps gathering those records, and the providers and health plans releasing them? Here’s what you need to know, including which requirements take effect now and which come later.
Continue Reading TEFCA’s new updated IAS Implementation SOP, version 3.0, takes effect August 3, 2026

42 CFR Part 2’s consent rules got a major update, but did New Jersey’s HIV confidentiality law get the memo? A decades-old cross-reference may leave New Jersey’s HIV consent requirements tied to the 1987 version of the federal rule. For providers and HIEs, the answer could affect both how they share records and their exposure to patient lawsuits.
Continue Reading Consent at a Crossroads: Has New Jersey’s HIV/AIDS Confidentiality Standard Changed in the Era of Part 2 Reform?

Time is up, and the enforcement infrastructure is now live. OCR’s complaint portal is open to 42 CFR Part 2, and Part 2 breach reporting is no longer a future workflow. A live portal changes behavior: it lowers the friction to file, increases complaint volume, and accelerates how quickly organizations receive the familiar “we have received a complaint, please explain” letter. If you are a Part 2 program, a QSO, or a lawful holder (including many HIPAA covered entities and business associates), this is the moment Part 2 stops being a policy project and becomes immediate operational exposure.
Continue Reading Time is Up! OCR Complaint Intake & Breach Reporting Go Live for 42 CFR Part 2

Epic’s new lawsuit casts the company as the white knight protecting patient records from alleged data thieves. For a company already facing antitrust claims over its own data-access practices, that is quite a wardrobe change. But will this fight make health information exchange safer, or leave everyone else afraid to share?
Continue Reading Epic the “White Knight”? Epic Sues for Alleged Unlawful Access to Patients Records

HTI-5 is calling out two things the market already knows: EHI is increasingly accessed through automation and AI, and “infeasible” has been doing suspiciously heavy lifting in some corners of the ecosystem. If you are an HIE/HIN, a developer of certified health IT, or a provider, these proposed information blocking changes tighten the exception playbook, put contract gating on notice, and make it harder to hide a “no” behind nicer paperwork.
Continue Reading HTI-5 and Information Blocking: Your Bots Are Covered, and Your Excuses Are Getting Smaller

ONC just dropped four new Information Blocking FAQs on December 19, 2025, and they go straight to the real pressure points: revenue-sharing dressed up as fees, “alternative manner” gamesmanship, and whether automation counts as access. These clarifications matter most where policy meets operations. If you build, sell, operate, or rely on interoperability, this is the set to read.
Continue Reading ONC Quietly Dropped Four (4) New Information Blocking FAQs

HHS has declared that the “warning period” for information blocking is over, putting HIEs, HINs, developers, and providers squarely in the path of active enforcement. With OIG empowered to levy million-dollar penalties, ONC able to strip certifications, and CMS now finalizing monetary disincentives for certain providers, the consequences are real and far-reaching. At the same time, long-standing practices, such as conservative privacy policies or restrictive BAAs, may suddenly collide with federal interoperability mandates. This article examines the new enforcement posture, the risks and dilemmas it creates, and what health information networks and their provider members must do to prepare.
Continue Reading Are You Blocking? The Coming Crackdown on Information Blocking: What It Means for HIE/HINs, Developers of Certified HIT, & Health Care Providers

Ever burned valuable time chasing down what feels like endless versions of 42 CFR Part 2? No more! Bookmark this for your one-stop place to go for copies of every single Notice of Proposed Rulemaking (NPRM) and Final Rule for 42 CFR Part 2, starting with the very first proposal in 1974! Whether you’re a compliance officer, privacy lawyer, or just a regs nerd who loves immediate access to the rules you need, this list has you covered. Bookmark it, share it, and breathe easy knowing you’ll never again waste hours digging through archives. You’re welcome. 😉
Continue Reading Bookmark This! Copies of All 42 CFR Part 2 Rules Published from 1974 to 2024

Starting February 16, 2026, Part 2 programs and providers will be required to report unauthorized disclosures of Part 2 information – specifically, any “acquisition, access, use, or disclosure” that violates 42 CFR Part 2. This is a major change that will significantly impact Part 2 programs. Let me explain why.
Continue Reading Beware! New Breach Reporting Obligations Under 42 CFR Part 2 — Even When HIPAA Wouldn’t Require It

On August 6, 2025, ONC unveiled the first public TEFCA Organizational Map, a tool that makes it possible to see which health systems are stepping into the national interoperability framework—and which are not. For some, this marks a milestone in transparency and progress; for others, it raises questions about strategy, governance, and whether more national data sharing is always a good thing. The uneven pace of adoption, particularly among Epic’s vast customer base, shows just how complicated the march into TEFCA has become.
Continue Reading From Dragging Feet to Dragged Along: The Uneven March Into TEFCA

On June 18, 2025, Judge Kacsmaryk of the U.S. District Court for the Northern District of Texas vacated key provisions of HHS’s HIPAA Privacy Rule that had imposed new federal protections for reproductive health care information. This means that HIPAA-covered entities must immediately stop requiring a HIPAA-compliant Attestation from requestors seeking PHI that includes (or is likely to include) reproductive health information. Covered entities must now also reevaluate their current processes for handling requests for PHI related to reproductive health information. However, if you operate in a state that has its own state-level reproductive privacy or provider shield law, those…
Continue Reading Regulatory Roller Coaster: District Court Judge Vacates HIPAA Reproductive Health Privacy Rule

HHS has opened the door to one of the biggest questions in health information law: should the TEFCA exception to the information blocking rules stay or go? The May 16, 2025 RFI asks whether this carve-out encourages participation in TEFCA or instead creates confusion and double standards for networks like Carequality, which already impose requirements stricter than HIPAA. With comments due June 16, stakeholders have just days to weigh in on a decision that could reshape the balance between nationwide interoperability and local control.
Continue Reading Does the TEFCA Exception Hinder Participation?